Identity & Access Management
API-Driven Identity & Access Management powered by WSO2
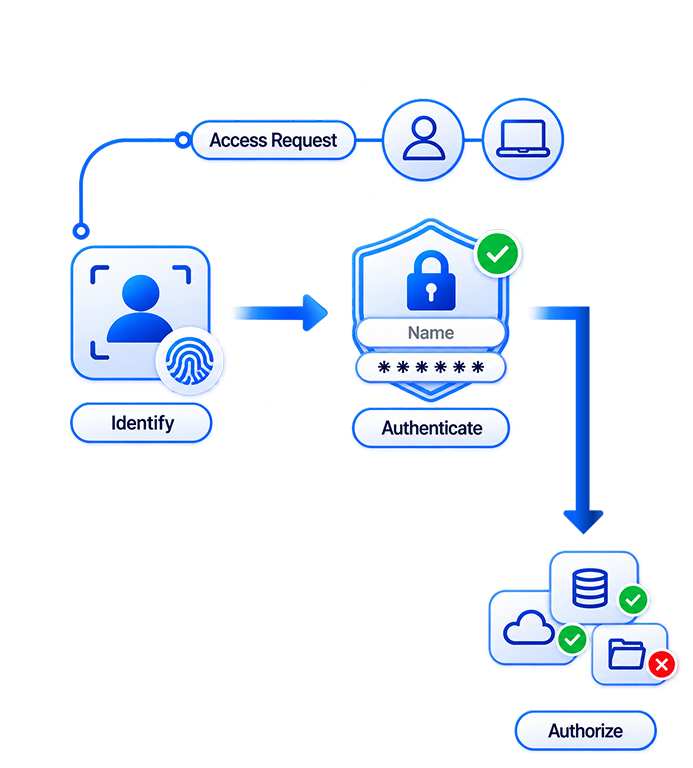
Secure your digital ecosystem with WSO2 Identity Server, an open-source, highly extensible IAM solution. We deliver robust Customer IAM (CIAM) and workforce identity management, providing frictionless single sign-on (SSO), strong multi-factor authentication (MFA), and centralized access control across your on-premises, cloud, and hybrid environments.
- Seamless Single Sign-On (SSO)
- Adaptive & Multi-Factor Authentication
- API & Microservices Security
- Centralized User Management
- Identity Federation
- Fine-Grained Access Control
What’s included
API-driven identity and access management across on-premises, cloud, and hybrid environments
- Seamless Single Sign-On (SSO)
Enable frictionless access across multiple applications using open standards like SAML, OAuth, and OpenID Connect (OIDC)
- Adaptive & Multi-Factor Authentication
Deploy strong, context-aware MFA and passwordless options like passkeys to adapt to user risk profiles
- API & Microservices Security
Secure modern applications with an API-driven, cloud-native identity framework built for deep extensibility
- Centralized User Management
Empower users with self-registration, account recovery, and robust administrative lifecycle controls
- Identity Federation
Bridge identities effortlessly across heterogeneous systems, social logins, and external identity providers
- Fine-Grained Access Control
Enforce strict Role-Based Access Control (RBAC) and privacy regulations like GDPR through centralized policies
The technical flow
Architecture Assessment
Evaluate existing identity stores, applications, and federation requirements
WSO2 Configuration
Deploy and configure the WSO2 Identity Server for your specific use cases
Application Integration
Connect enterprise applications via SAML, OAuth2, and OIDC
Policy & MFA Rollout
Define access policies and roll out multi-factor authentication
Engagement
How We Deliver It
What you gain
- Frictionless User Experience
Users log in once to access all authorized resources seamlessly
- Reduced Helpdesk Burden
Self-service password resets and account recovery cut IT costs
- Zero Vendor Lock-in
Leverage the power and flexibility of open-source technology
- Regulatory Compliance
Easily meet GDPR and other privacy mandates with centralized control
- Credential Attack Defense
Eliminated risk of credential stuffing and lateral movement
- Single Sign-On Experience
Seamless single-login user experience across all enterprise applications
Technologies we work with
- IAM
- IGA
- MDM
- ZTNA
- MFA
- FIDO2
- SCIM
Standards & frameworks we align to
- NIST 800-63
- ISO 27001
- SOC 2 ACCESS CRITERIA
- HIPAA SECURITY RULE
Ready to strengthen your Identity Security posture?
Tell us what you’re protecting. We’ll help you secure it.