Privileged Access Management
Comprehensive Privileged Access Management powered by Segura
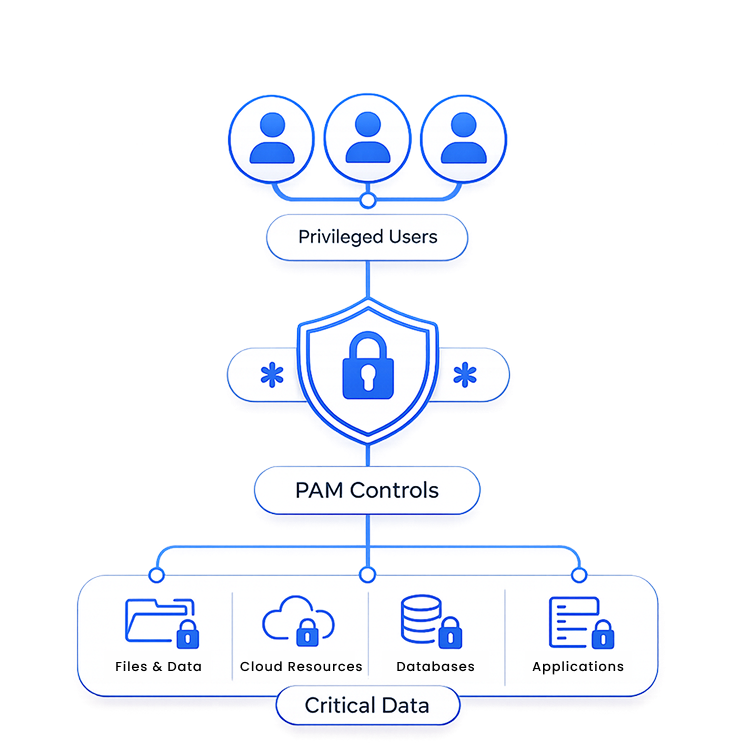
Take control of your most critical accounts with Segura PAM. Designed to discover, secure, and audit privileged identities across cloud, on-premises, and DevOps environments, Segura eliminates standing privileges and mitigates insider threats through zero-trust principles, secure credential vaulting, and advanced session monitoring.
- Digital Credential Vaulting
- Privileged Session Management (PSM)
- Just-in-Time (JIT) Access
- Automated Asset Discovery
- Granular Command Control
- Compliance & Governance
What’s included
Discover, secure, and audit privileged identities across cloud, on-premises, and DevOps environments
- Digital Credential Vaulting
Securely store, manage, and automatically rotate passwords and SSH keys in a military-grade encrypted vault
- Privileged Session Management (PSM)
Monitor, proxy, and record every privileged session with high-compression video for complete auditability and forensics
- Just-in-Time (JIT) Access
Eliminate standing privileges by granting granular, time-bound access only when explicitly required
- Automated Asset Discovery
Continuously scan your IT environment to map and identify unmanaged assets and shadow credentials
- Granular Command Control
Proactively block unauthorized or harmful commands during live sessions before they can be executed
- Compliance & Governance
Streamline audit reporting for GDPR, PCI DSS, SOX, and ISO 27001 with comprehensive access tracking
The technical flow
Asset & Account Discovery
Scan the environment to identify all privileged accounts and shadow IT
Vaulting & Rotation
Onboard credentials into the encrypted vault and enable automatic rotation
Session Proxy Setup
Configure PSM for SSH, RDP, and web sessions with recording enabled
JIT Policy Enforcement
Implement Just-in-Time access rules to eliminate standing privileges
Engagement
How We Deliver It
What you gain
- Mitigate Insider Threats
Prevent unauthorized access and lateral movement within the network
- Simplified Audits
Generate compliance reports instantly with full session video logs
- Rapid Deployment
Achieve faster time-to-value with Segura's streamlined architecture
- Protect Critical Assets
Secure intellectual property, financial data, and core infrastructure
- Credential Attack Defense
Eliminated risk of credential stuffing and lateral movement
Technologies we work with
- CREDENTIAL VAULTING
- PRIVILEGED SESSION MANAGEMENT (PSM)
- JUST-IN-TIME ACCESS
- SSH KEY MANAGEMENT
Standards & frameworks we align to
- NIST 800-63
- ISO 27001
- SOC 2 ACCESS CRITERIA
- HIPAA SECURITY RULE
Ready to strengthen your Identity Security posture?
Tell us what you’re protecting. We’ll help you secure it.