Endpoint & Extended Detection and Response
Advanced Detection. Unified Visibility. Rapid Response
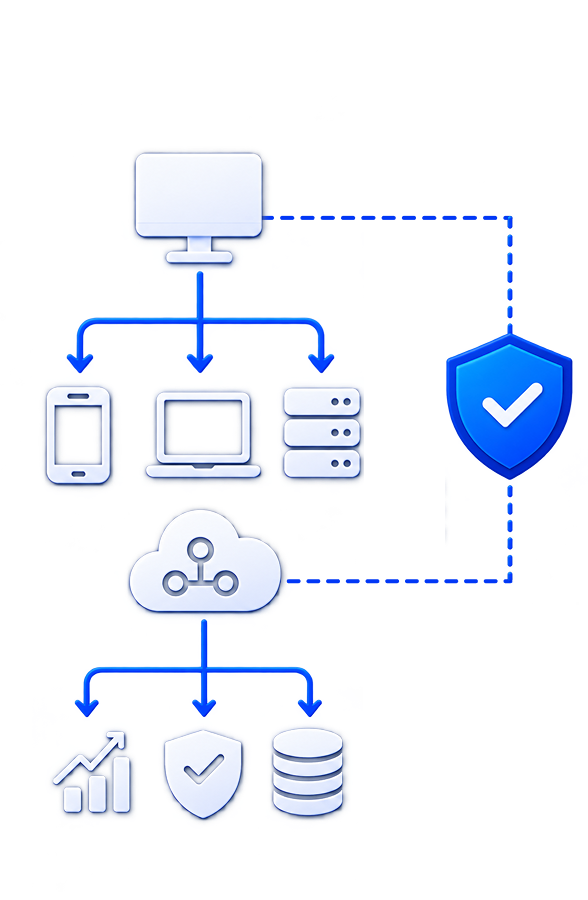
Traditional antivirus solutions are no longer sufficient to address today's evolving threat landscape. Our EDR and XDR solutions provide continuous security monitoring, behavioral threat detection, investigation, threat hunting, and automated response. EDR protects and monitors individual endpoints, while XDR extends detection and response across the broader security ecosystem, including endpoints, networks, identities, email, and cloud workloads.
- Continuous Endpoint Monitoring
- Behavioral Threat Detection
- Cross-Domain Correlation (XDR)
- Automated Incident Response
- Threat Hunting
- MITRE ATT&CK Mapping
What’s included
Continuous security monitoring, behavioral threat detection, investigation, threat hunting, and automated response
- Continuous Endpoint Monitoring
Monitor process creation, file activity, network connections, user activity, registry changes, and command-line execution in real time
- Behavioral Threat Detection
Detect advanced threats using behavioral indicators, not just known signatures, including credential dumping, lateral movement, and fileless attacks
- Cross-Domain Correlation (XDR)
Correlate telemetry from endpoints, network, email, identity, cloud, and applications to understand the full attack chain rather than isolated events
- Automated Incident Response
Isolate endpoints, terminate malicious processes, quarantine files, block connections, and disable compromised accounts to contain threats instantly
- Threat Hunting
Proactively search for hidden threats using IP addresses, file hashes, processes, user accounts, and MITRE ATT&CK techniques across historical data
- MITRE ATT&CK Mapping
Map observed behaviors to adversary techniques including Initial Access, Lateral Movement, Credential Access, and Exfiltration for structured investigation
The technical flow
Assessment
Evaluate the existing endpoint and security environment to understand gaps
Architecture & Deployment
Design an EDR/XDR architecture and deploy endpoint agents across the environment
Detection Engineering
Develop and configure detection rules, behavioral policies, and security use cases
Integration
Integrate EDR/XDR with SIEM, SOAR, firewalls, identity systems, and threat intelligence platforms
Continuous Improvement
Continuously tune detections and workflows based on emerging threats and operational findings
Engagement
How We Deliver It
What you gain
- Detect Earlier
Identify threats at the earliest stage using behavioral detection before attackers can achieve their objectives
- Investigate Deeper
Reconstruct the full attack timeline, from phishing email to privilege escalation, across multiple security layers
- Respond Faster
Automated containment actions reduce the time between detection and isolation from hours to minutes
- Ransomware Protection
Detect abnormal file encryption, shadow copy manipulation, and privilege escalation to contain ransomware before it spreads
- Sub-Minute Containment
Sub-minute threat detection and isolation capabilities
- Holistic Visibility
Holistic visibility spanning hybrid multi-cloud infrastructure
Technologies we work with
- EDR
- XDR
- BEHAVIORAL ANALYTICS ENGINES
- MITRE ATT&CK MAPPING
Standards & frameworks we align to
- MITRE ATT&CK
- NIST CSF DETECT & RESPOND
- ISO 27035
Ready to strengthen your Detection & Response posture?
Tell us what you’re protecting. We’ll help you secure it.