Network Detection & Response
See What's Happening Across Your Network
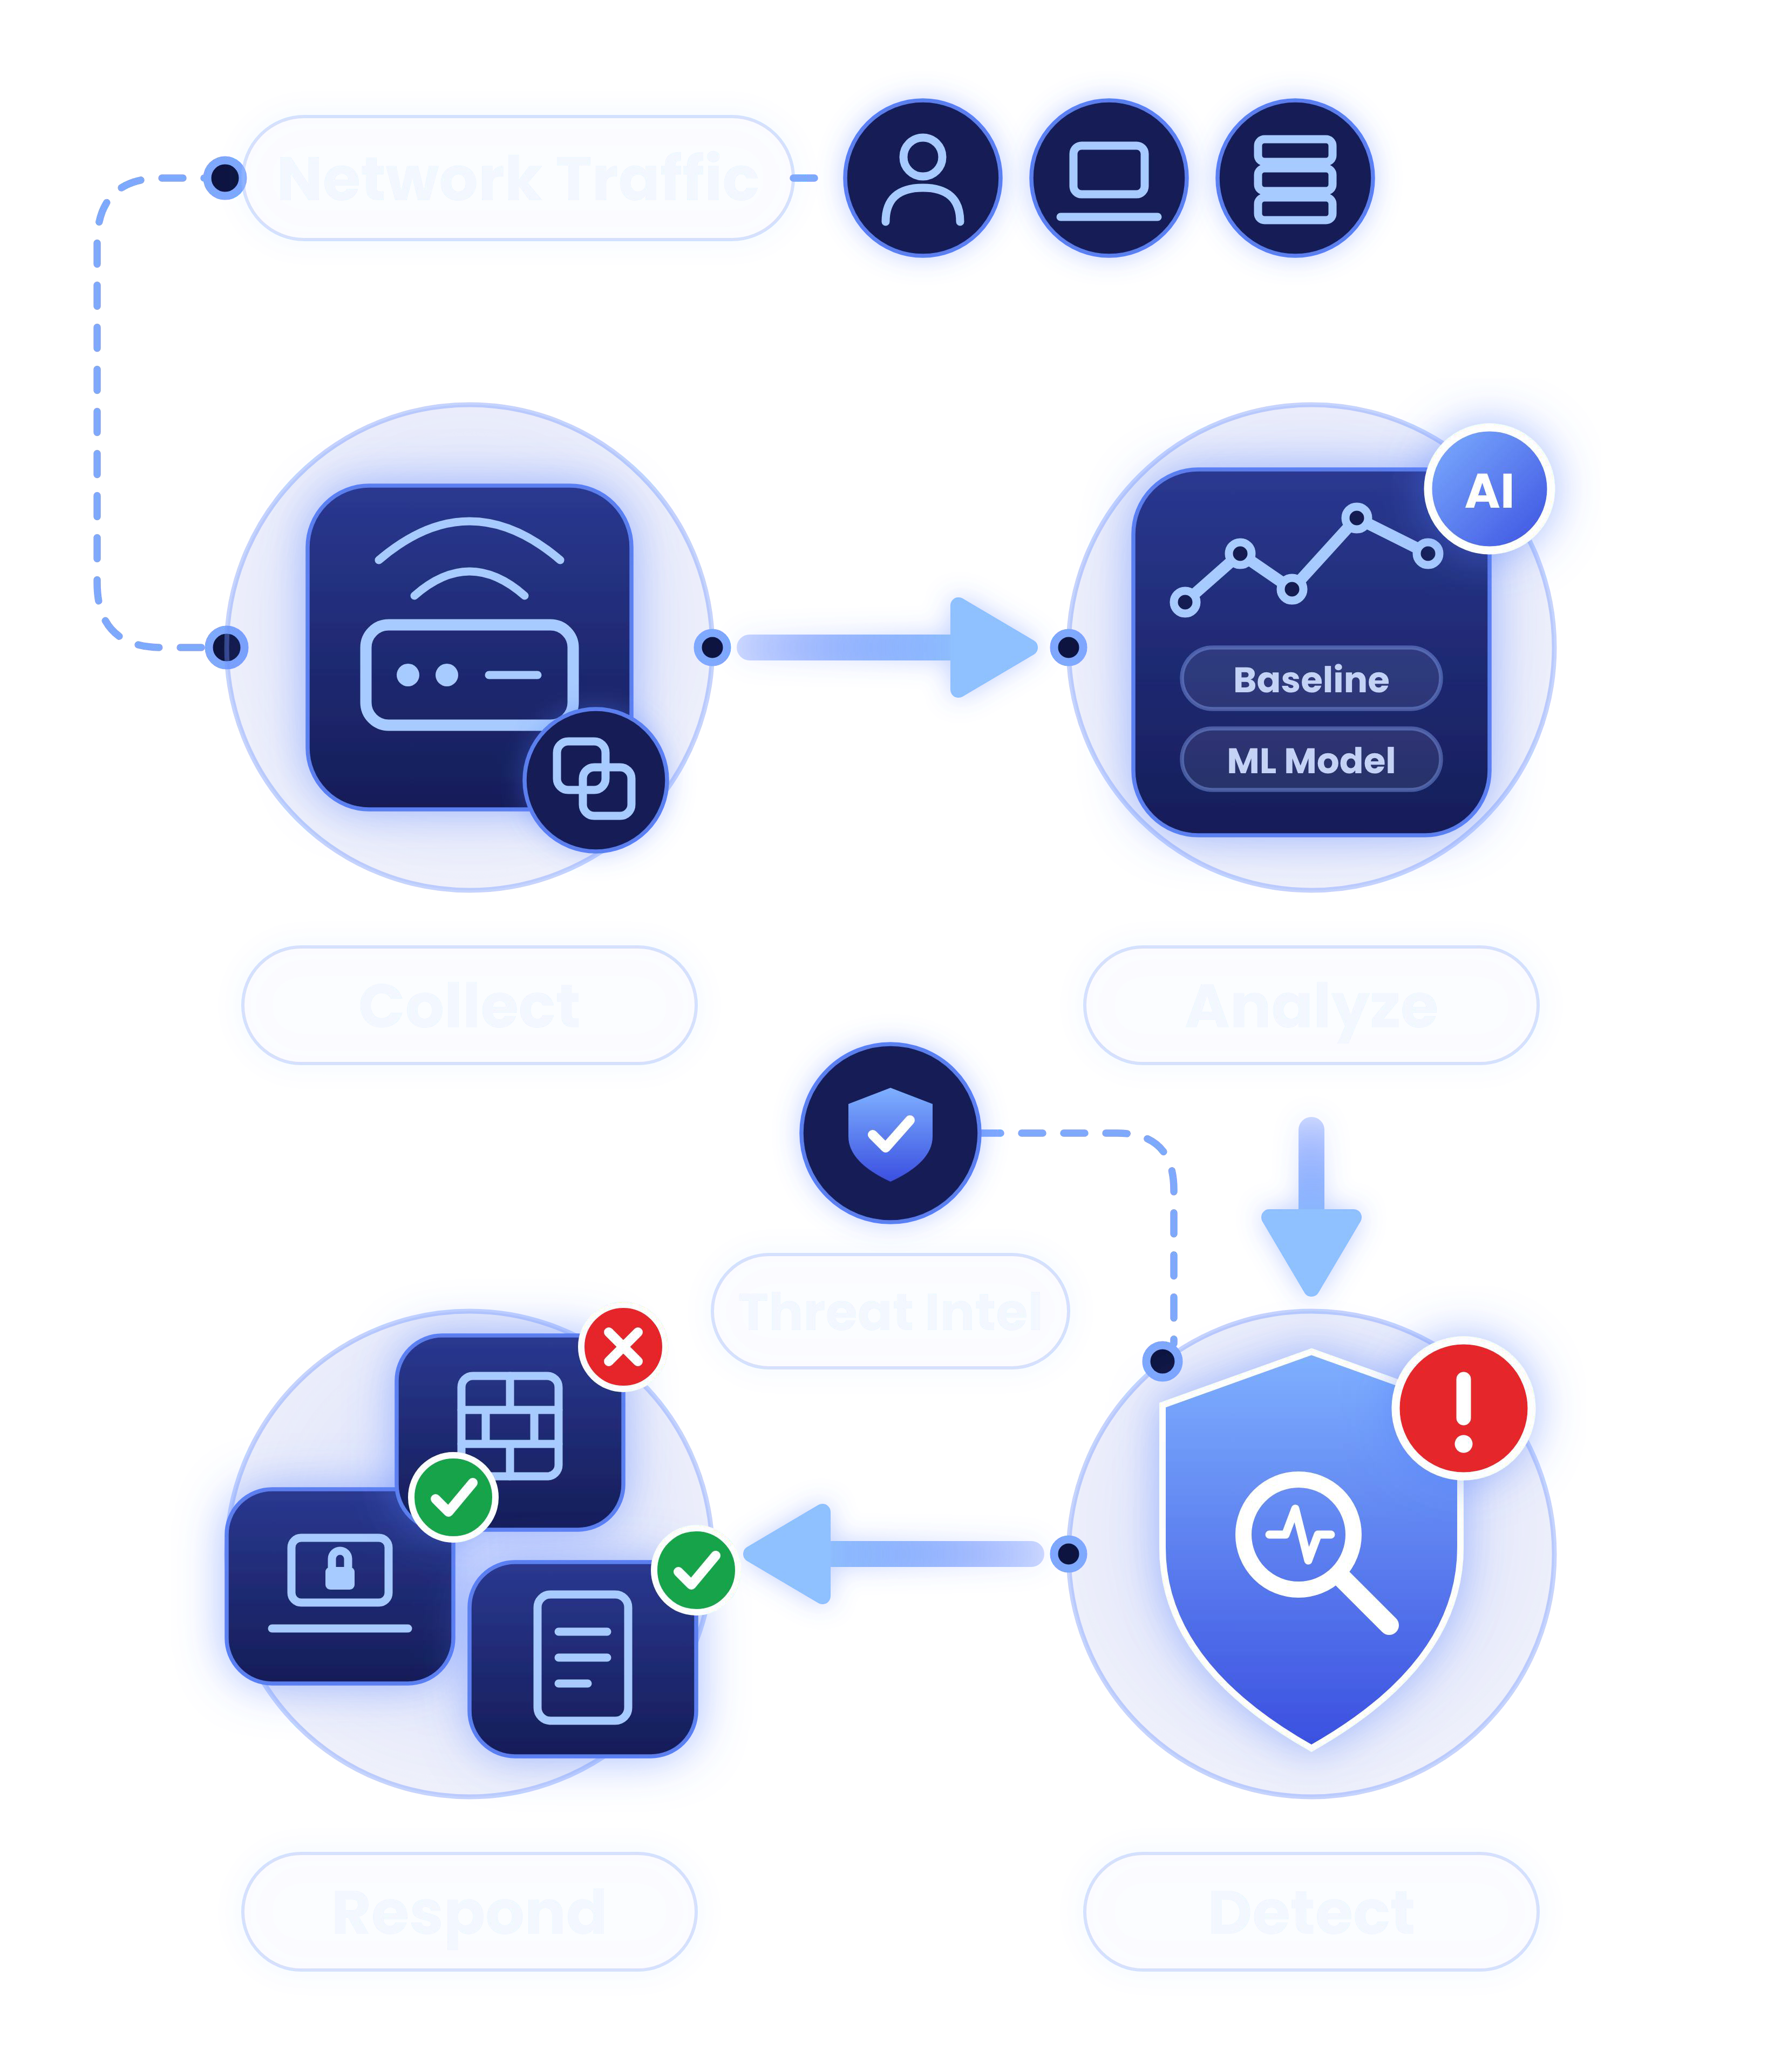
Modern cyberattacks rarely remain confined to a single endpoint. Attackers move through networks, establish command-and-control channels, discover internal systems, escalate privileges, and attempt to exfiltrate sensitive information. NDR provides continuous visibility into network activity, analyzes network behavior, detects suspicious and malicious communications, and enables security teams to investigate and respond to threats across the entire network, including threats that bypass endpoint and perimeter controls.
- Behavioral Network Detection
- Command & Control Detection
- Lateral Movement Detection
- Data Exfiltration Detection
- DNS Security Monitoring
- Encrypted Traffic Analysis
What’s included
Continuous visibility into network activity, analyzing network behavior and detecting suspicious and malicious communications
- Behavioral Network Detection
Identify deviations from normal network behavior, unusual communication patterns, beaconing, abnormal data volumes, and unexpected destinations, without relying solely on signatures
- Command & Control Detection
Identify C2 activity by analyzing repeated outbound connections, beaconing patterns, suspicious DNS queries, and communications with known malicious infrastructure
- Lateral Movement Detection
Detect suspicious internal system-to-system communication via SMB, RDP, SSH, WinRM, LDAP, and Kerberos that indicates attacker movement across the network
- Data Exfiltration Detection
Identify suspicious data movement through abnormal outbound transfers, unexpected protocols, encrypted connections, and data transfers outside normal business patterns
- DNS Security Monitoring
Analyze DNS activity for rare domains, newly observed domains, algorithmically generated patterns, DNS tunneling, and communications with known malicious domains
- Encrypted Traffic Analysis
Detect potentially suspicious encrypted communications by analyzing connection frequency, destination reputation, session duration, traffic volume, and behavioral characteristics
The technical flow
Network Assessment
Identify critical network segments, communication paths, assets, and monitoring requirements
Visibility Architecture
Determine appropriate network telemetry sources, TAPs, SPAN ports, sensors, flow data, and cloud telemetry
NDR Deployment
Deploy and configure network detection capabilities across on-premises, cloud, and hybrid environments
Detection Engineering
Develop use cases for C2, lateral movement, reconnaissance, exfiltration, and DNS threats
SIEM & SOAR Integration
Forward network events into SIEM for centralized correlation and automate response workflows via SOAR
Engagement
How We Deliver It
What you gain
- Detect C2 & Lateral Movement
Identify attacker activity that occurs over the network even when endpoint controls have been bypassed
- Accelerate Investigations
Answer Who, What, Where, When, and How about every suspicious communication for faster incident analysis
- Improve Threat Hunting
Proactively search network telemetry using IPs, domains, behavioral patterns, and MITRE ATT&CK techniques
- Strengthen SOC Capabilities
Complement EDR/XDR and SIEM with network-layer visibility to create a true defense-in-depth architecture
- Holistic Visibility
Holistic visibility spanning hybrid multi-cloud infrastructure
Technologies we work with
- NDR
- DEEP PACKET INSPECTION
- ENCRYPTED TRAFFIC ANALYTICS
- DNS SECURITY MONITORING
Standards & frameworks we align to
- MITRE ATT&CK
- NIST CSF DETECT & RESPOND
- ISO 27035
Ready to strengthen your Detection & Response posture?
Tell us what you’re protecting. We’ll help you secure it.