Threat Intelligence
Turn Threat Data Into Actionable Security Intelligence
Cyber threats are constantly evolving. Attackers change infrastructure, modify malware, rotate domains and IP addresses, exploit emerging vulnerabilities, and develop new techniques to bypass traditional security controls. Threat Intelligence transforms raw threat data into meaningful, contextual, and actionable intelligence that helps organizations anticipate, detect, investigate, and respond to cyber threats.
- Strategic Threat Intelligence
- Tactical Intelligence (TTPs)
- Indicators of Compromise (IoCs)
- Vulnerability Intelligence
- Threat Actor Intelligence
- Digital Risk Monitoring
What’s included
Turn external and internal signals into informed defensive actions across the cybersecurity environment
- Strategic Threat Intelligence
High-level intelligence for executive leadership and CISOs covering major threat trends, threat actor activity, industry-specific threats, geopolitical risks, and emerging attack techniques
- Tactical Intelligence (TTPs)
Understand how adversaries operate, credential dumping, lateral movement, PowerShell execution, persistence, C2 methods, mapped to MITRE ATT&CK for improved detection coverage
- Indicators of Compromise (IoCs)
Receive timely IoCs including malicious IPs, domains, URLs, file hashes, email indicators, and host artifacts to integrate directly into security controls for detection
- Vulnerability Intelligence
Understand which vulnerabilities are being actively exploited, which threat actors are using them, and which assets in your environment are at risk, to prioritize remediation by actual exposure
- Threat Actor Intelligence
Profile threat actor groups, their motivations, targeted sectors, preferred techniques, malware, infrastructure, and historical activity, to understand who may target your organization
- Digital Risk Monitoring
Identify lookalike domains, brand impersonation, phishing campaigns, fraudulent accounts, credential leaks, and suspicious certificates targeting your organization externally
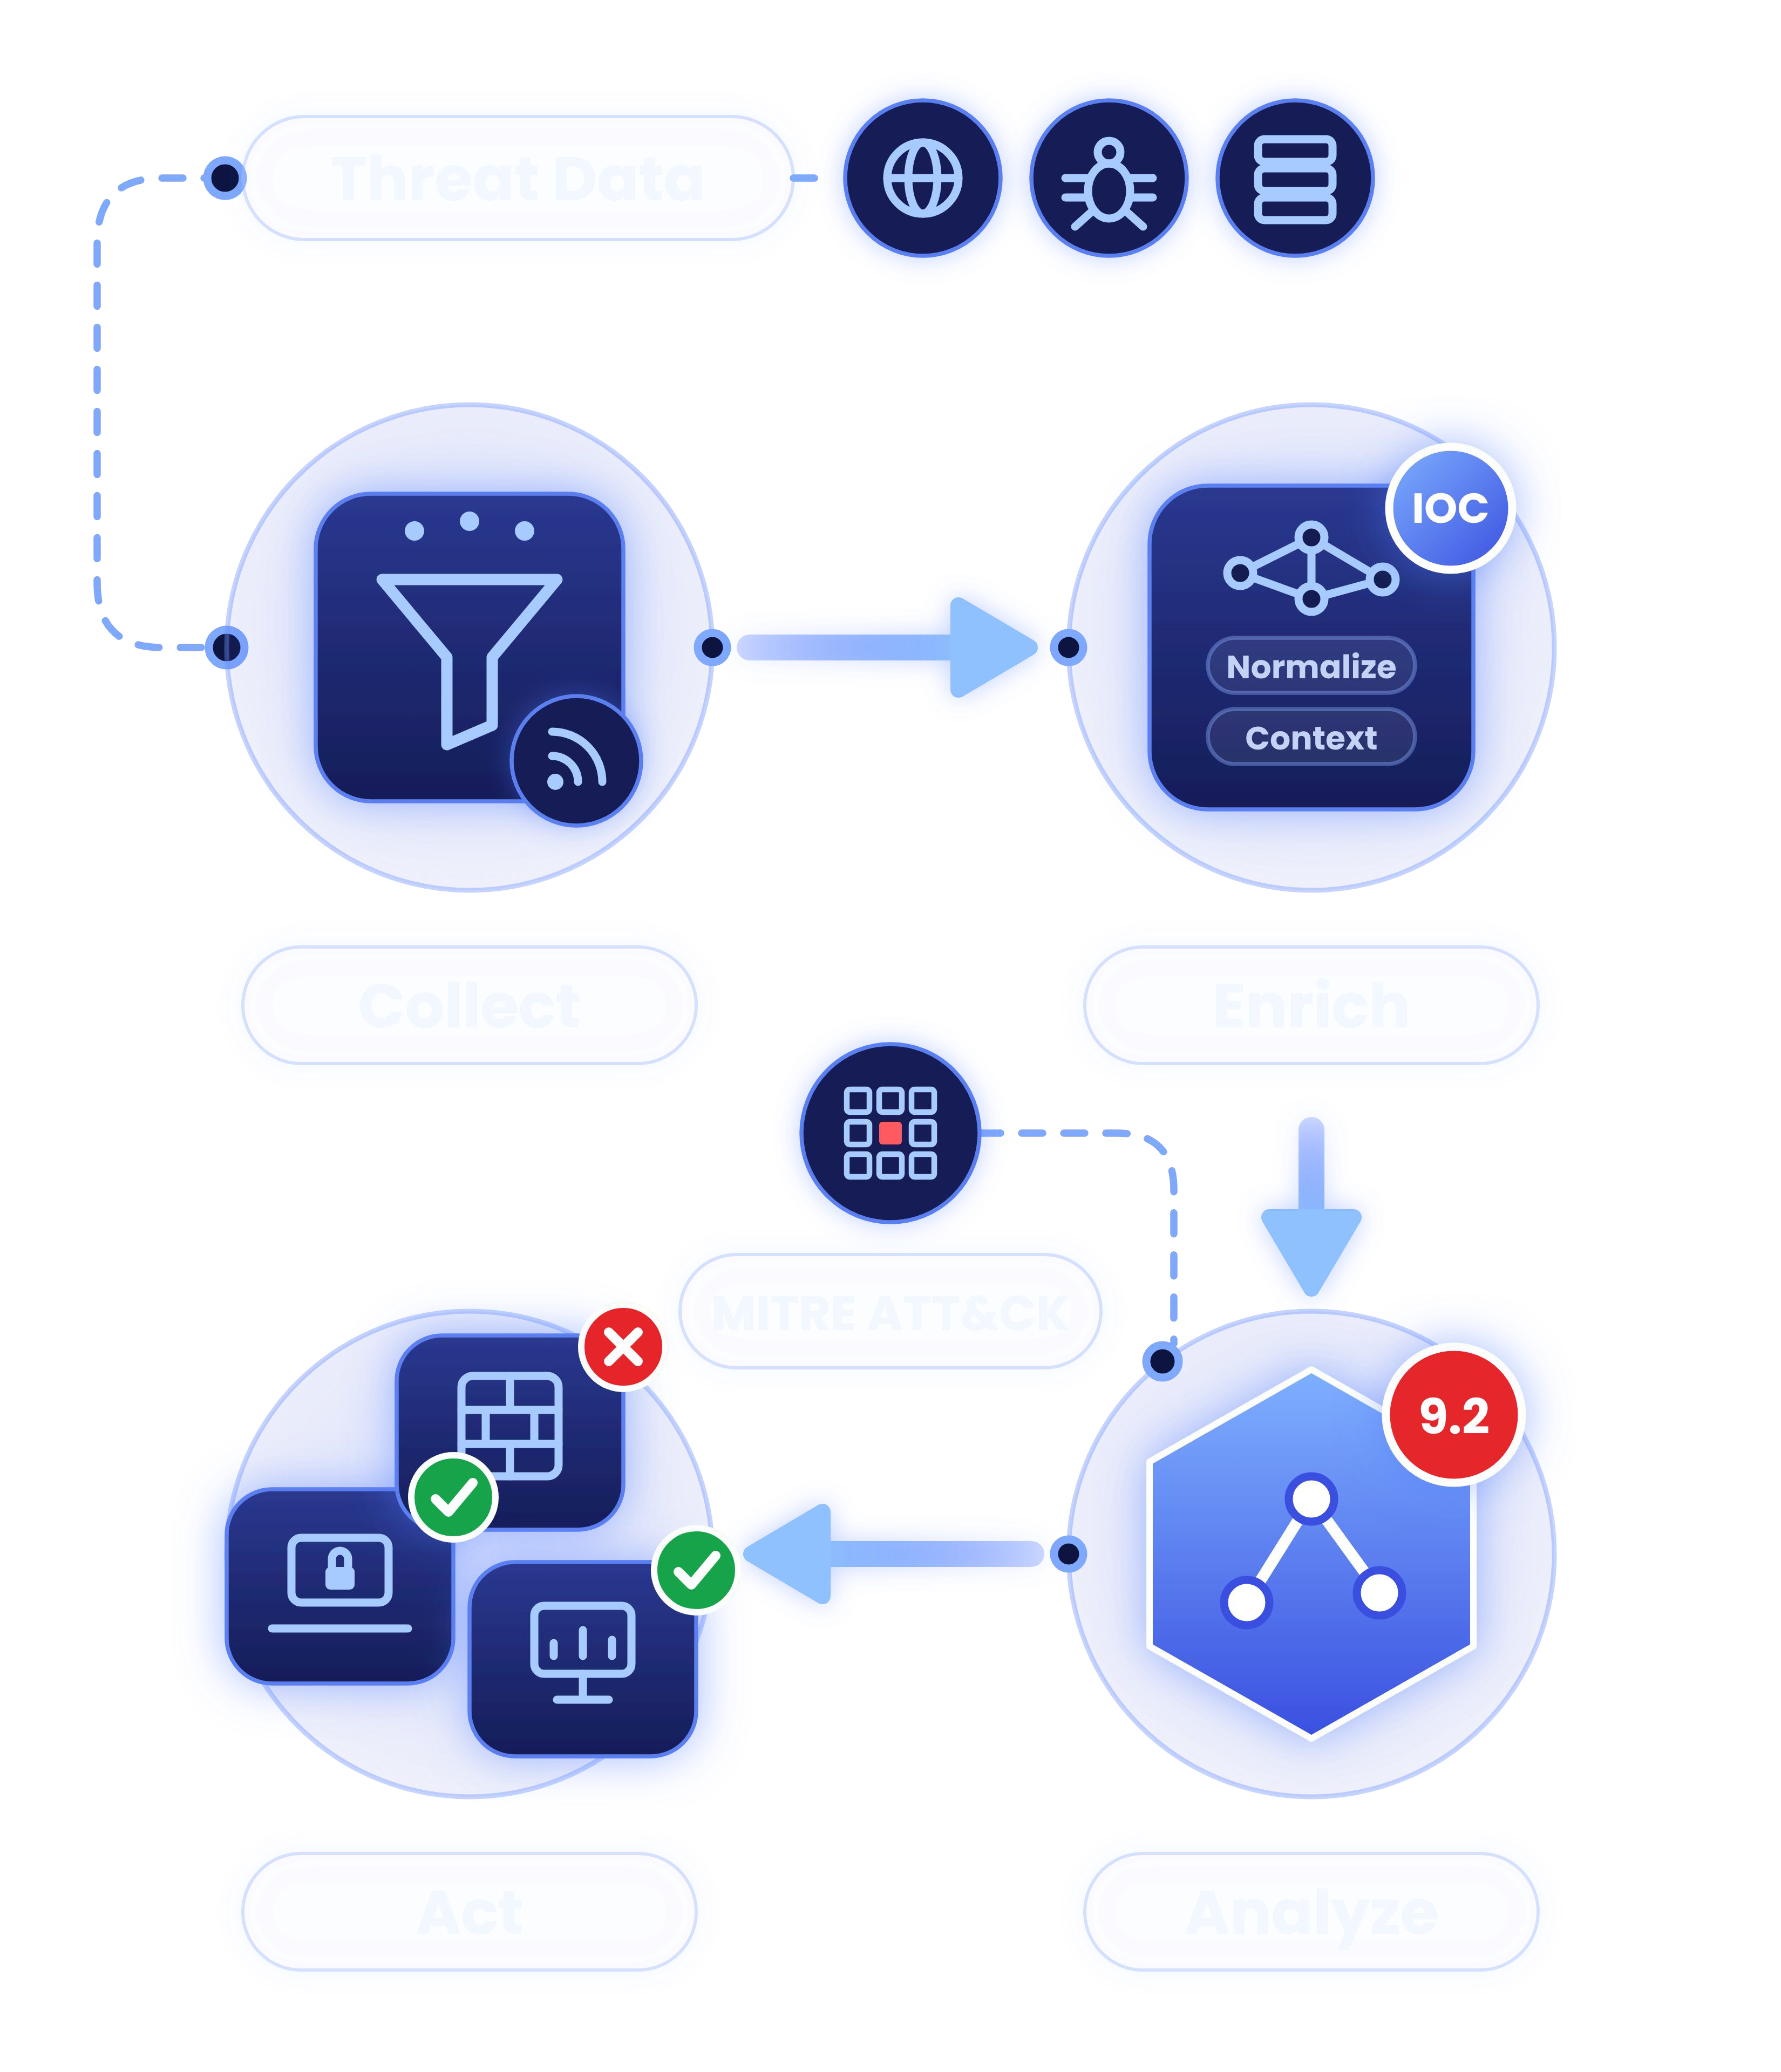
The technical flow
Define Requirements
Identify the intelligence questions that matter most, who targets us, what techniques are emerging, which vulnerabilities are actively exploited
Collect & Process
Gather from open-source, commercial, government, vendor, and internal sources, then normalize, validate, and structure the data
Enrich & Analyze
Add reputation context, correlate indicators, identify relationships between campaigns and actors, and determine organizational relevance
Operationalize
Integrate intelligence into SIEM, EDR/XDR, NDR, and SOAR platforms so detections are enriched and response actions are automated
Hunt & Improve
Use intelligence-driven hypotheses to proactively search for threats, then feed findings back to continuously improve the intelligence lifecycle
Engagement
How We Deliver It
What you gain
- Detect Known Malicious Infrastructure
Automatically correlate SIEM, EDR, and NDR events against threat intelligence feeds to surface C2, malware, and attacker infrastructure instantly
- Prioritize Vulnerabilities by Risk
Focus remediation on vulnerabilities that are actively exploited in the wild, not just on CVSS severity score alone
- Accelerate Incident Response
During an incident, quickly identify responsible threat actors, related infrastructure, malware families, and additional indicators to search for
- Enable Proactive Defense
Transform intelligence from passive information into active hunting campaigns that find threats before they trigger an automated alert
Technologies we work with
- THREAT INTELLIGENCE FEEDS
- THREAT INTELLIGENCE GRAPH
- DARK WEB CRAWLERS
Standards & frameworks we align to
- MITRE ATT&CK
Ready to strengthen your Detection & Response posture?
Tell us what you’re protecting. We’ll help you secure it.