Security Orchestration, Automation & Response
Accelerate Security Operations Through Intelligent Automation
Modern security teams face an overwhelming number of alerts, repetitive tasks, and increasingly sophisticated cyber threats. Our SOAR solutions help organizations streamline security operations by integrating security technologies, automating repetitive workflows, and enabling faster, more effective incident response, through partnerships with IBM and Fortinet.
- Security Orchestration
- Workflow Automation
- Security Playbooks
- Threat Intelligence Correlation
- Automated Incident Response
- Case Management
What’s included
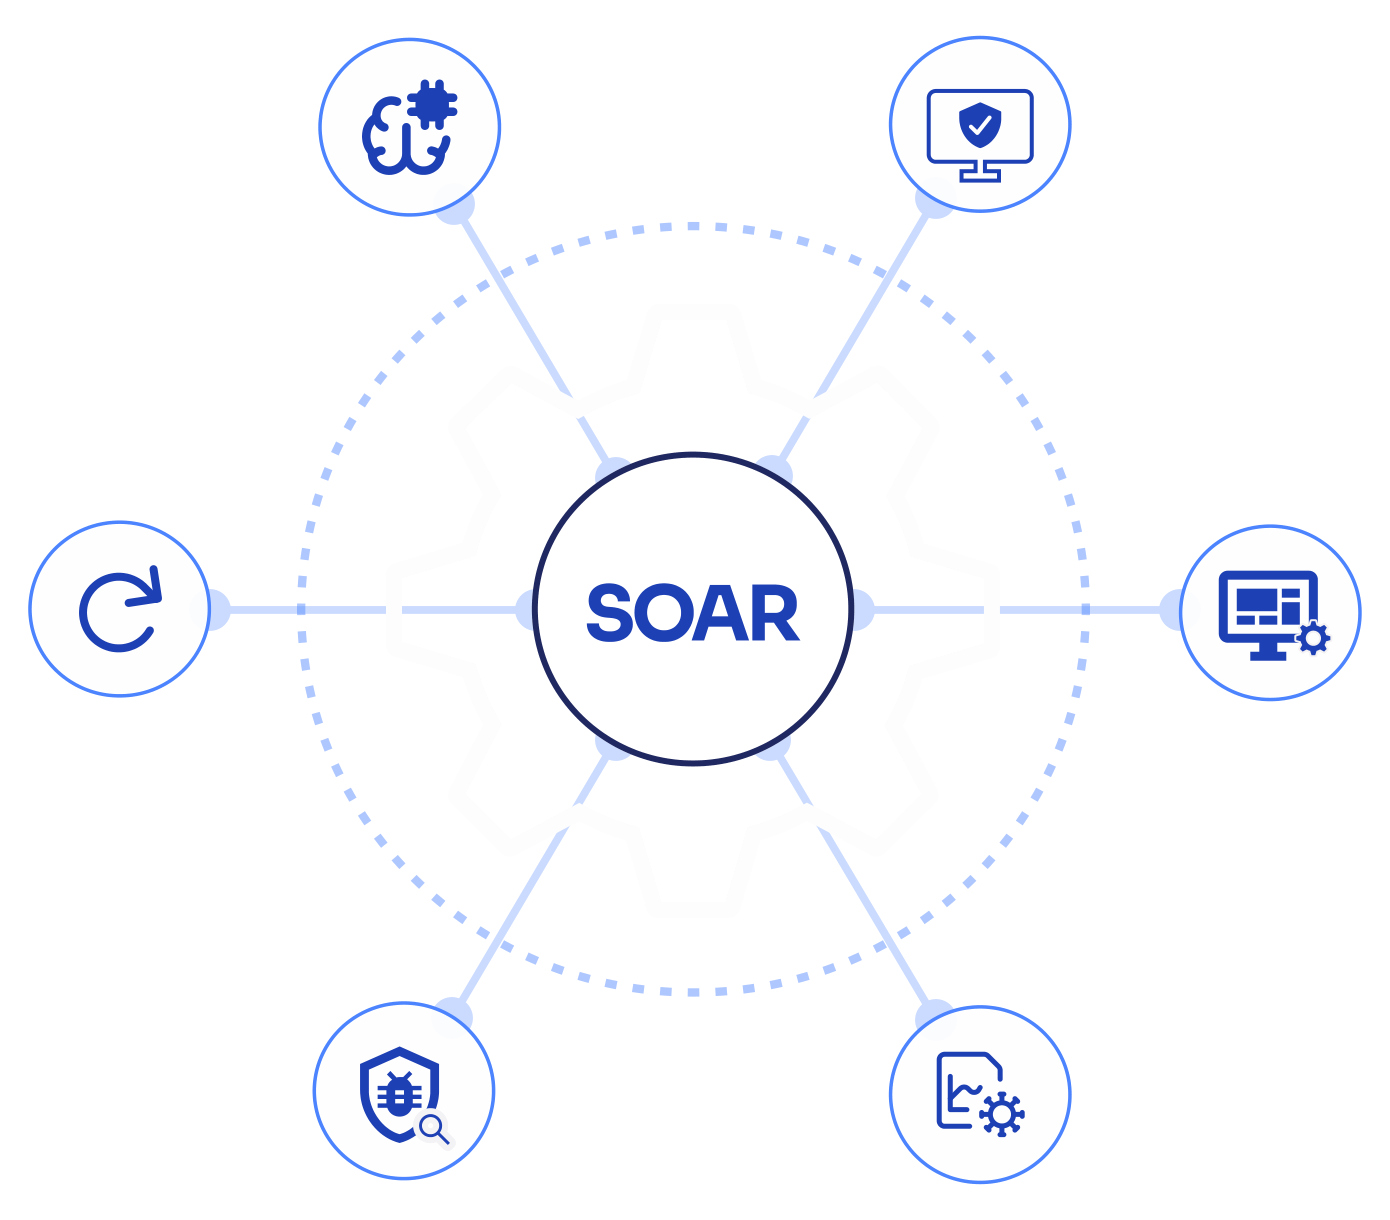
Streamline security operations by integrating security technologies and automating repetitive workflows
- Security Orchestration
Integrates multiple security technologies and systems to enable coordinated security operations across your entire environment
- Workflow Automation
Automates repetitive tasks such as alert enrichment, triage, and case management, reducing manual effort and improving response times
- Security Playbooks
Standardize response procedures with predefined workflows for phishing, malware, compromised accounts, and vulnerability incidents
- Threat Intelligence Correlation
Enrich alerts using internal and external threat intelligence sources for faster, more informed decision-making
- Automated Incident Response
Execute automated actions such as blocking IPs, isolating endpoints, disabling accounts, and quarantining emails instantly
- Case Management
Automatically create, update, and assign incident tickets to manage incidents from detection through to closure
The technical flow
Detect
Security event is received from SIEM, EDR, or another integrated tool
Analyze & Enrich
SOAR automatically gathers contextual data, IP reputation, user activity, and threat intelligence
Automate
Predefined playbooks trigger automated response actions without human intervention
Respond & Recover
Security team focuses on strategic decisions as SOAR handles containment and remediation
Engagement
How We Deliver It
What you gain
- Faster Response Times
Automate repetitive actions and drastically reduce Mean Time to Respond (MTTR)
- Reduced Alert Fatigue
Filter, prioritize, and enrich alerts automatically so analysts focus on real threats
- Consistent Processes
Standardize investigations and response activities using playbooks to eliminate human error
- Scalable Security Operations
Handle increasing alert volumes without proportionally increasing analyst headcount
- Sub-Minute Containment
Sub-minute threat detection and isolation capabilities
Technologies we work with
- SOAR
- PLAYBOOK ORCHESTRATION ENGINES
- SIEM & EDR INTEGRATIONS
- CASE MANAGEMENT SYSTEMS
Standards & frameworks we align to
- MITRE ATT&CK
- NIST CSF DETECT & RESPOND
- ISO 27035
Ready to strengthen your Detection & Response posture?
Tell us what you’re protecting. We’ll help you secure it.