Security Information & Event Management
Turn Security Data Into Actionable Intelligence
Modern organizations generate massive volumes of security data across endpoints, networks, servers, applications, cloud environments, and identity systems. Our SIEM solutions provide centralized security monitoring, intelligent event correlation, threat detection, investigation, and real-time visibility across your entire digital environment, through partnerships with leading cybersecurity technology providers including IBM and Fortinet.
- Centralized Log Management
- Intelligent Threat Detection
- Incident Investigation
- Security Analytics
- Threat Hunting
- Alert Management
What’s included
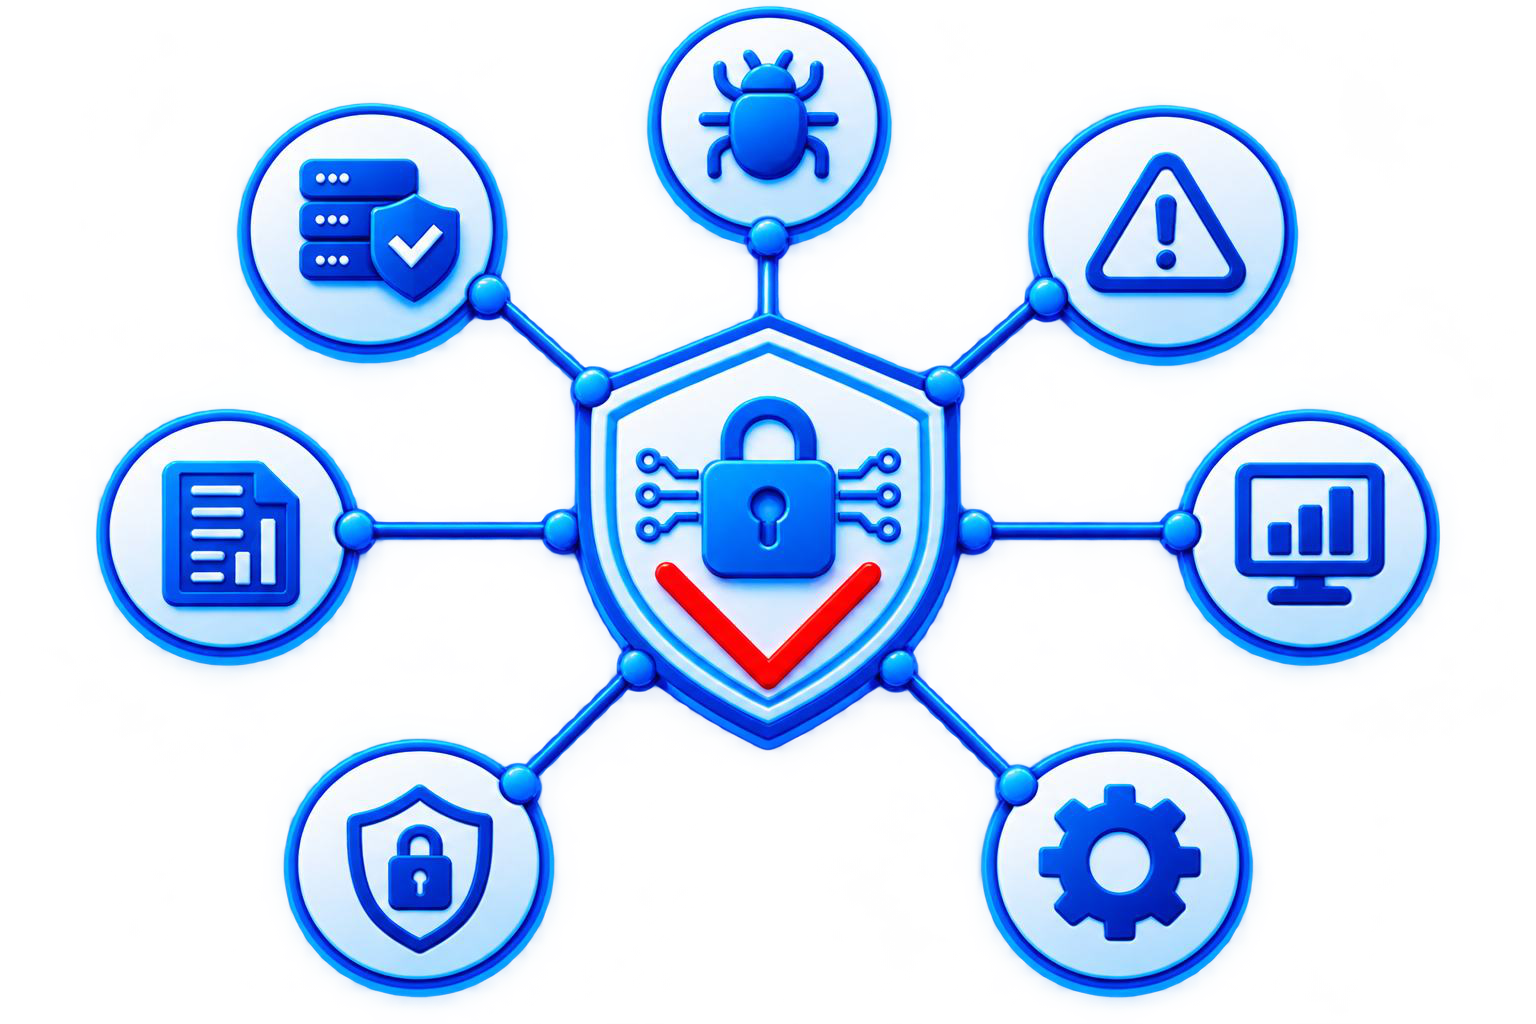
Centralized security monitoring, intelligent event correlation, threat detection, investigation, and real-time visibility
- Centralized Log Management
Bring security events and logs from across your organization into a centralized monitoring environment
- Intelligent Threat Detection
Continuously analyze security events to identify suspicious activities, anomalies, and potential indicators of compromise
- Incident Investigation
Give security teams the context they need to investigate incidents efficiently with timelines, users, and IP indicators
- Security Analytics
Transform raw security events into meaningful insights that support faster decision-making
- Threat Hunting
Search across historical security data to proactively identify suspicious behavior and previously undetected threats
- Alert Management
Prioritize and manage security alerts based on severity, context, and organizational risk
The technical flow
Collect
Centralized collection and storage of security logs and events
Normalize & Correlate
Connect related events from different systems to identify attack patterns
Detect
Identify malicious and suspicious activity using advanced analytics
Investigate & Respond
Reconstruct attack timelines and support rapid incident response
Engagement
How We Deliver It
What you gain
- Centralized Visibility
Ask "What is happening across our entire environment?" instead of looking at siloed systems
- Reduce Alert Noise
Correlate individual signals to provide the bigger picture and focus on real threats
- Prioritize High-Risk Events
Focus security operations on incidents that present the greatest risk to the organization
- Detect Attack Patterns
Identify complex attacks involving compromised credentials, lateral movement, and privilege escalation
- Sub-Minute Containment
Sub-minute threat detection and isolation capabilities
- Less Alert Fatigue
Vastly reduced alert fatigue for internal security teams
Technologies we work with
- SIEM
- THREAT FEEDS
- SOAR INTEGRATION
- MITRE ATT&CK MAPPING
Standards & frameworks we align to
- MITRE ATT&CK
- NIST CSF DETECT & RESPOND
- ISO 27035
Ready to strengthen your Detection & Response posture?
Tell us what you’re protecting. We’ll help you secure it.